Discover · feedburner.com

Microsoft’s November 2026 Patch Tuesday addresses 1093 CVEs (CVE-2026-124194)

JUST™ Creative feedburner.com

Microsoft addresses 1093 CVEs in the eleventh Patch Tuesday of 2026.

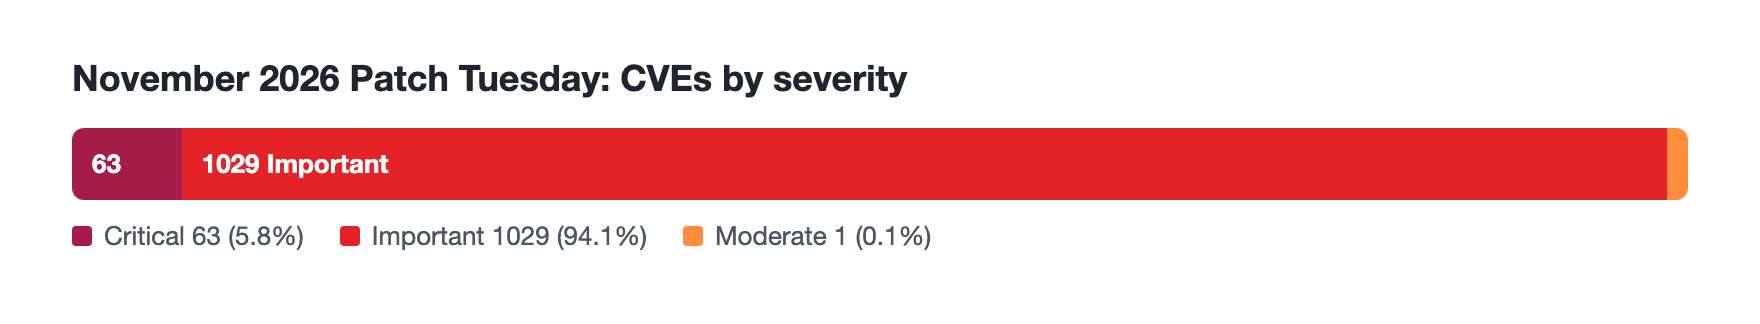
Microsoft patched 1093 CVEs in its November 2026 Patch Tuesday release, with 63 rated critical, 1029 rated as important, and one rated as moderate.

More ways to use this
Open on another device
Scan this QR code to open the same public page

Scan to open this page. Your saved notes and account access are not included.
Download QR code

Open the page link

Names and references

  1. November — person

In the piece

CVE-2026-124194 | Microsoft Outlook spoofing vulnerabilityCVE-2026-124194 is a spoofing vulnerability in Microsoft Outlook. It received a CVSSv3 score of 6.5 and is rated moderate. An attacker could exploit this vulnerability by convincing a target to open a crafted Microsoft Office file. Successful exploitation…JUST™ CreativeCVE-2026-118146 | Windows Active Directory Domain Services remote code execution vulnerabilityCVE-2026-118146 is an RCE vulnerability affecting Windows Active Directory Domain Services. It received a CVSSv3 score of 8.8 and is rated as critical. An authenticated attacker could exploit an incorrect authorization in Active Directory Domain Services to…JUST™ CreativeCVE-2026-120002 | Microsoft SharePoint Server elevation of privilege vulnerabilityCVE-2026-120002 is an EoP vulnerability affecting Microsoft SharePoint Server. It received a CVSSv3 score of 9.9 and is rated as important. An authenticated attacker could exploit an incorrect authorization in Microsoft Office SharePoint to elevate privileges…JUST™ CreativeCVE-2026-118207 | Microsoft Exchange Server remote code execution vulnerabilityCVE-2026-118207 is an RCE vulnerability affecting Microsoft Exchange Server. It received a CVSSv3 score of 8.8 and is rated as critical. An authenticated attacker could send malformed input to Microsoft Exchange Server, causing code to execute over a network.…JUST™ CreativeCVE-2026-119952 | Windows Schannel remote code execution vulnerabilityCVE-2026-119952 is an RCE vulnerability affecting Windows Schannel. It received a CVSSv3 score of 8.1 and is rated as critical. An unauthenticated attacker could exploit an observable timing discrepancy in Windows Schannel to execute code over a network.…JUST™ CreativeAdditional Notable CVEsJUST™ CreativeTenable SolutionsJUST™ CreativeGet more informationJUST™ Creative

Keep going

Each of these is read from what this estate already kept: the feed a piece came through, the publisher behind it, the credits and topics the publisher printed. None of it is a recommendation, an identity or a record kept anywhere else.

More like this

Also from JUST™ Creative

  1. Able2Shell: Frequently asked questions for reported N-able N-central zero-day vulnerabilitiesResearch Special Operations feedburner.com
  2. U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacksChristopher Day feedburner.com
  3. php2shell one week later: Why one exploit doesn’t work everywhereJoshua Martinelle, Thomas Cappetta feedburner.com
  4. Whole-of-state defense: How SLED agencies can secure critical infrastructure in the AI eraChristopher Day feedburner.com
  5. Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)Satnam Narang feedburner.com
  6. Discover and remediate PHP2Shell exposure with TenableTeam Tenable feedburner.com