OAuth authentication for webhook destinations will soon be available by default for workspaces with the compliance security profile enabled
docs.databricks.com databricks.com
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Starting on or after December 20, 2026, OAuth authentication for webhook destinations will be available by default for workspaces with the compliance security profile enabled, subject to the requirements for regions and compliance standards.
Use OAuth 2.0 client credentials to send notifications to an endpoint that requires an access token. Databricks obtains the token from the configured OAuth token endpoint and uses it to authenticate the notification request. Existing webhook destinations retain their configured authentication.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
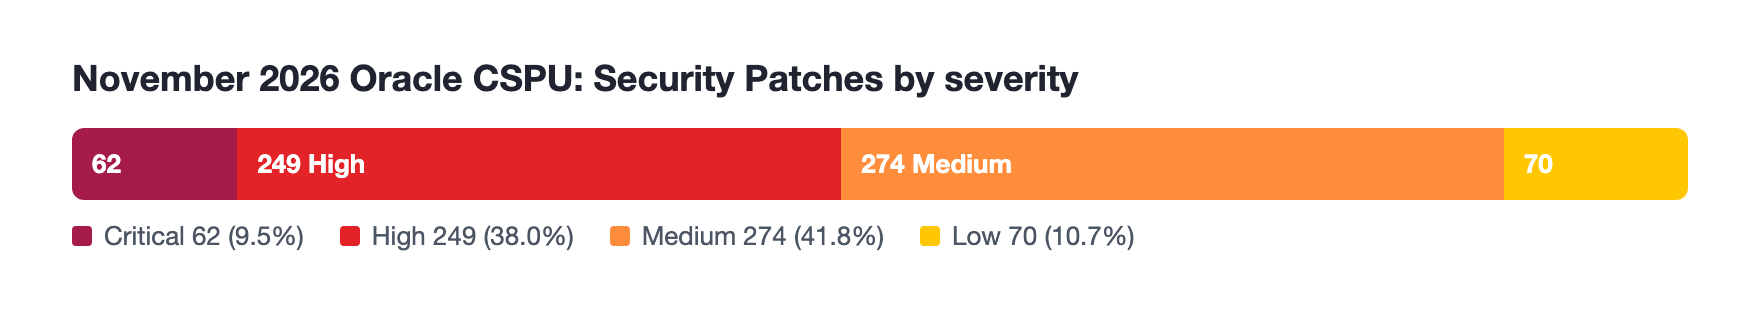 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)